Audit trails in document processing: what to log and who gets access
For operations, compliance and IT teams that process financial, health or insurance documents: what a useful audit trail records, how to set roles so people see only what they need, and what the rules expect.
Key takeaways
- An audit trail is a chronological, tamper-evident record of who did what to a document, when, and what changed.
- In document AI, every step writes an entry: received, extracted with a confidence score, reviewed or corrected, approved and exported.
- A useful trail has attribution, before-and-after values, reasons, search, export and a retention schedule. A raw log dump has events without that context.
- Role-based access control gives each person only the documents and actions their job needs, and the audit trail shows those limits held.
- The rules set the floor: HIPAA requires audit controls and unique user IDs, the FTC Safeguards Rule requires logging authorized users' activity, and the PCI DSS card standard requires 12 months of logs.
On this page
- What an audit trail records
- How audit trails work in document AI systems
- What separates a useful audit trail from a log dump
- Role-based access control: who can see and do what
- Which rules call for audit trails and access control
- How Docsumo handles audit logging and review
- The bottom line
- Frequently asked questions
An audit trail in document processing is a chronological, tamper-evident record of every action taken on a document: who received, viewed, extracted, corrected, approved or exported it, when, and what changed. It lets you rebuild how any document was handled, which is what an auditor or regulator will ask for. Role-based access control is its partner: it limits each person to the documents and actions their job needs, and the trail shows those limits held.
This guide covers what to record, how the trail builds up, what makes it useful, how to set roles and which rules apply.
What an audit trail records#
NIST defines an audit trail as a chronological record that lets you reconstruct the sequence of activities behind an event, from start to finish. For a document, each entry answers five questions:
Who
The person, by their own login, or the system or service account that acted. Never a shared account.What
The action: received, viewed, extracted, corrected, approved, exported or deleted.When
A timestamp from a synchronized clock, so events from different systems line up.What changed
The field, its value before and after, and the model's confidence score.Why
A reason code or note for every override, rejection or manual correction.
A log file records events. An audit trail is evidence: structured, complete and protected from edits.
How audit trails work in document AI systems#
Each stage writes its own entries, from the moment a file arrives until its data reaches another system.
- Email inbox
- Uploads
- API
- 01Received
- 02Extracted with confidence
- 03Reviewed or corrected
- 04Approved
- 05Exported
Here's one invoice's trail:
| Time (UTC) | Who | Event | Detail |
|---|---|---|---|
| 09:14:27 | System, email intake | Received | INV-1847.pdf, file hash recorded |
| 09:14:41 | Extraction model | Extracted | Due date 04/15/2026, confidence 0.62 |
| 09:31:05 | Reviewer, AP team | Corrected | Due date 04/15/2026 → 05/15/2026; reason: invoice date read as due date, terms Net 30 |
| 10:02:18 | Approver, AP manager | Approved | Total $1,742.35 |
| 10:02:19 | System, API | Exported | Sent to the ERP |
Nothing in the trail is edited later. A correction is a new entry that keeps the old value, so the original extraction stays visible.
What separates a useful audit trail from a log dump#
A logging tool pointed at an application records events. It becomes an audit trail when it can answer an auditor's question in minutes:
- AttributionEvery entry names one person or one service account. Shared logins make the trail useless.
- Before and after valuesCorrections keep the original value, the new value and the field they belong to.
- ReasonsOverrides, rejections and manual corrections carry a reason code or a note.
- Tamper evidenceEntries are append-only and hashed or signed, and any change to the log is itself logged.
- SearchYou can filter by document, user, field, action and date, and ideally by field value.
- ExportAn auditor can get the entries for a document or a period as a usable file, without engineering work.
- RetentionEntries are kept as long as the strictest rule that applies to you, then deleted on schedule.
- ReviewSomeone reads the log. HIPAA requires regular review of activity records, not just their collection.
Role-based access control: who can see and do what#
Role-based access control (RBAC) ties permissions to roles rather than to people: you define what a reviewer can do once, then assign people to the role. It enforces least privilege, giving each user only the access their tasks need, and every action in the trail maps to a role allowed to take it. Typical roles in a document workflow:
Admin
Manages users, roles and settings. Doesn't need to approve documents.Reviewer
Sees the documents assigned to them and corrects extracted fields.Approver
Approves or rejects, but can't edit the fields they approve, which keeps duties separate.Viewer or auditor
Read-only access to documents and the audit trail, for internal audit, accountants and compliance.
Scope each role by document type and workflow stage as well as action, and by field where your tool allows it: an invoice reviewer shouldn't see loan files, and a data entry clerk may not need bank account numbers. The pattern is the same for banking, healthcare or construction documents. Four mistakes undo it:
| Mistake | What goes wrong | Fix |
|---|---|---|
| Role creep | People keep old permissions as their jobs change | Change the role with the job, and review access on a schedule |
| Shared accounts | The trail can't say which person acted | One login per person, contractors included |
| Over-broad roles | Contractors and interns get full-time staff access | Narrow roles, such as "Contractor, invoices only" |
| No offboarding | Accounts stay active after people leave or projects end | Disable access the day the job ends, then check the log for later use |
Which rules call for audit trails and access control#
No one rule covers every document workflow, but several require an audit trail's parts, depending on the documents you handle:
| Rule | Applies to | What it asks for | Retention it sets |
|---|---|---|---|
| HIPAA Security Rule | Healthcare providers, health plans, clearinghouses and their business associates | Audit controls, unique user IDs and regular review of activity records | Documentation: 6 years |
| FTC Safeguards Rule (GLBA) | Non-bank financial institutions, such as mortgage lenders and brokers | Access limited to the customer information each user needs; authorized users' activity logged | Customer data disposed of within 2 years of last use, with exceptions |
| Interagency guidelines (GLBA) | Banks | Access controls, segregation of duties and monitoring, where appropriate | Not specified |
| PCI DSS v4 | Businesses that store, process or transmit card data | Access by job function, reviewed every 6 months; every user's access to card data logged | Logs: 12 months, the latest 3 at hand |
| Sarbanes-Oxley Section 404 | US public companies | A yearly assessment of internal control over financial reporting | Auditors' records: 7 years |
| GDPR | Personal data of people in the EU | Personal data kept no longer than needed | No fixed period |
The rules pull in different directions: GDPR and the FTC Safeguards Rule push you to delete data you no longer need, while HIPAA and PCI DSS set minimums. Agree one schedule per document type with your compliance team.
How Docsumo handles audit logging and review#
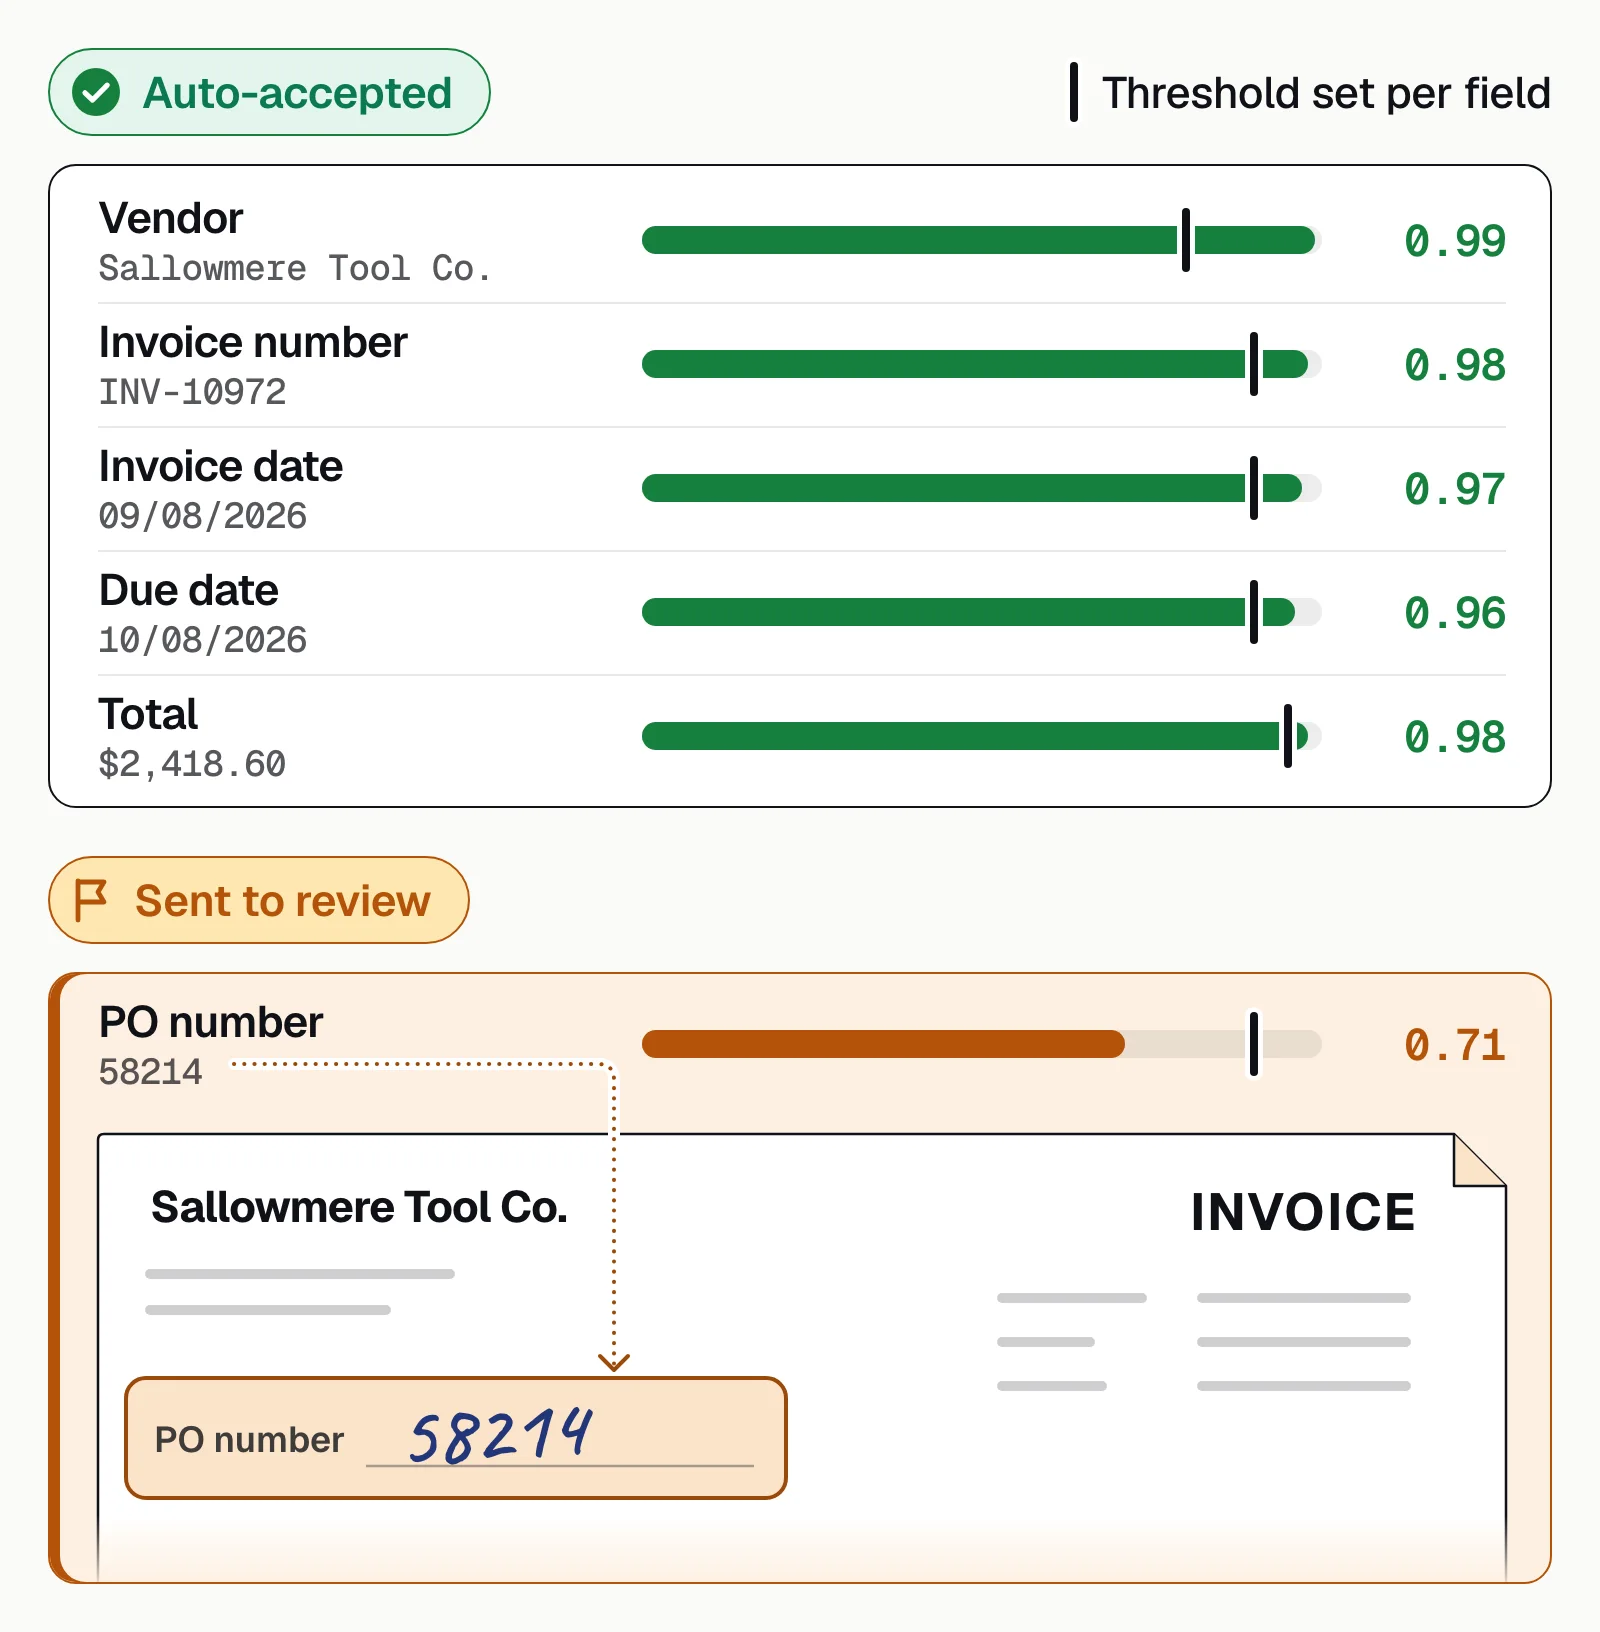
Docsumo includes audit logging on its Business plan, and it routes invoices for approval on the same plan. Fields the model is unsure about go to a person: confidence thresholds are set per field, clicking a field highlights its source line on the page, and reviewer corrections improve the model.
Access is controlled with role-based permissions, single sign-on and multi-factor authentication, and data is encrypted in transit (TLS) and at rest (AES-256). Docsumo is SOC 2 Type 2 audited, ISO/IEC 27001:2022 certified and supports HIPAA and GDPR (security page). It doesn't set your retention schedule or run your access reviews: those stay with your compliance team. More on review and approval steps in document workflows, and on thresholds in human-in-the-loop review.
The bottom line#
An audit trail turns "we processed it" into evidence: who did what, when, and what changed, for every document. Pair it with roles that give people only the access their jobs need, keep entries as long as your strictest rule requires, and read the log instead of just collecting it.
Book a demo with a few of your own documents, or start a free trial.
Frequently asked questions#
What is an audit trail in document processing?
A chronological, tamper-evident record of every action on a document: who received, viewed, extracted, corrected, approved or exported it, when, and what changed. It lets you show an auditor exactly how a document was handled.
Can audit logs be altered?
Not in a well-built audit trail. Entries should be append-only and hashed or signed, so any change is detectable, and any attempt to change the log is itself logged. If users can edit or delete entries, it isn't an audit trail.
How long should you keep audit logs?
It depends on the rules you're under. PCI DSS requires 12 months of audit log history, with the latest 3 months immediately available. HIPAA requires security documentation to be kept 6 years, and many teams keep audit logs as long. GDPR sets no fixed period but says personal data shouldn't be kept longer than needed.
What is role-based access control for banking documents?
It means giving bank and lending staff access to customer documents by role, such as processor, underwriter or auditor, so each person sees only what their job needs. For non-bank lenders, the FTC Safeguards Rule requires limiting each user to the customer information they need and logging their activity; banks follow similar interagency guidelines.
What should document processing software with role-based access control include?
Roles you can scope by document type and by action (view, edit, approve, export), one login per person, separation between the people who correct data and those who approve it, and an audit trail of every action by user. For accounts payable, check that approvers can't edit the invoices they approve.
Does Docsumo keep an audit trail?
Docsumo includes audit logging on its Business plan. Fields the model is unsure about go to a person for review, with confidence thresholds set per field, and reviewer corrections improve the model. See security for its SOC 2 Type 2 and ISO/IEC 27001:2022 details.
Sources
- NIST CSRC Glossary: audit trail
- NIST CSRC Glossary: role-based access control
- NIST CSRC Glossary: least privilege
- 45 CFR 164.312: HIPAA technical safeguards, audit controls and unique user identification (Cornell LII)
- 45 CFR 164.308: HIPAA administrative safeguards, information system activity review (Cornell LII)
- 45 CFR 164.316: HIPAA documentation requirements (Cornell LII)
- 16 CFR 314.4: FTC Safeguards Rule, elements of an information security program (Cornell LII)
- FTC: FTC Safeguards Rule, what your business needs to know
- 12 CFR Part 364, Appendix B: Interagency Guidelines Establishing Information Security Standards (Cornell LII)
- PCI Security Standards Council: PCI DSS v4.0 SAQ D for Merchants (requirements 7.2, 10.2 and 10.5.1)
- PCI Security Standards Council: PCI DSS v4.0.1 published (no added or deleted requirements)
- 15 U.S.C. 7262: Sarbanes-Oxley Act Section 404, management assessment of internal controls (Cornell LII)
- 17 CFR 210.2-06: Retention of audit and review records (Cornell LII)
- Regulation (EU) 2016/679 (GDPR), Article 5(1)(e): storage limitation
First published . Last updated .